

01
A public authority or body
Local authorities, government-funded bodies, public institutions and public service providers.
A registered DPO with regulatory experience, available for a predictable monthly fee and with capacity tailored to your organisation. Expert oversight of GDPR compliance, so you can focus on your business.
Data protection in expert hands. A registered DPO with regulatory experience, taking the burden of compliance off your shoulders.
Adjust the sliders and answer the questions to see your estimated monthly fee.
This estimate is indicative. We confirm the monthly fee and scope of service in a tailored proposal following a free initial consultation.
Understand the likely costs. Answer a few questions for an instant estimate, then we will work through the details together.
A Data Protection Officer (DPO) provides independent expert oversight of your organisation’s personal data processing. They advise management and staff, monitor compliance, support impact assessments and data subject requests, coordinate privacy incident response and act as the contact point for Hungary’s data protection authority, NAIH.
GDPR Articles 37–39 govern the DPO’s appointment and duties. The authority must be notified of the appointment and contact details must be made publicly available.
The DPO may be an employee or an external expert engaged under a service agreement; the GDPR expressly permits both arrangements.
Under the GDPR, a DPO must be appointed where the organisation:
Local authorities, government-funded bodies, public institutions and public service providers.
Examples include extensive CCTV, online behavioural tracking and profiling, fleet tracking, telecommunications or credit assessment processing, and direct marketing to a large customer base.
This may include healthcare providers, private clinics, laboratories, pharmacies, insurers, health funds, occupational health and recruitment companies, and educational or social care institutions.
Hungary’s Information Act may require appointment in additional cases. A voluntarily appointed DPO is subject to the same requirements for independence, expertise and notification as a mandatory appointment.
GDPR obligations apply independently of a DPO appointment. Organisations need appropriate processing records and notices, timely breach notifications where required, and responses to data subject requests. These duties often fall informally to management, HR or IT. An outsourced DPO gives them expert attention within agreed monthly capacity and supports regulatory enquiries and complaints. Many clients choose this voluntarily because privacy matters to the trust of customers, partners and employees.
Where appointment is mandatory, failing to appoint a DPO can itself attract fines of up to €10 million or 2% of worldwide annual turnover. Breaches of the GDPR’s core principles may attract up to €20 million or 4%. NAIH can also restrict or suspend processing and publish its decisions. In practice, mishandled incidents and unanswered data subject requests can quickly escalate into regulatory complaints.
Restrictions and public decisions NAIH may suspend processing as well as impose fines, and publishes its decisions.
Updated: September 2026
A named zemITis expert becomes your registered DPO, identified on your website and in your privacy notices. The monthly fee typically includes 8–20 dedicated expert hours, depending on size, processing activities and maturity. Your proposal specifies the agreed capacity and covers the following work:
Your registered DPO is a named expert supported by information security and compliance colleagues. Documents undergo independent peer review before delivery. This provides broader expertise and continuity, reducing reliance on a single person while regulatory deadlines continue to apply.
Our DPO service can be combined with NIS2, ISO/IEC 27001 and ISO/IEC 42001 (AI management) projects, as well as our outsourced security officer service.
The DPO acts independently, receives no instructions about how to carry out their statutory duties and reports directly to senior management. They must not determine the purposes and means of the processing they oversee, which commonly creates conflicts for managing directors and heads of IT, HR or marketing. Identifying, training and safeguarding the independence of a suitable internal person can be a significant burden for a role requiring only a few hours a month.
| Szempont | In-house DPO (employee) | zemITis kiszervezett DPO |
|---|---|---|
| Independence and conflicts of interest | Decision-making roles may conflict with DPO duties; the organisation must demonstrate competence and independence | An external, independent specialist with a clearly defined role |
| Professional expertise | Typically a legal or IT background supplemented by self-directed learning | A lawyer and cybersecurity law specialist with five years of regulatory experience, backed by information security experts |
| Getting started | Selection, training and employment arrangements can take months | Ready to start after signing; we prepare the NAIH notification |
| Availability | No built-in cover for leave, illness or resignation, while breach and request deadlines continue to apply | A team supports the registered DPO, ensuring continuity |
| Protection of the DPO role | A DPO cannot be dismissed or penalised for performing their duties, which must be reflected in internal employment arrangements | A service agreement with a clear scope and termination terms |
| Regulatory liaison | A learning curve during the first investigation | Established familiarity with regulatory procedures from inside the authority |
| Cost | Salary and employer contributions for a part-time responsibility, plus ongoing training | A predictable monthly fee aligned with actual needs |
| Objectivity | Internal relationships and pressure from colleagues | An external, evidence-based perspective informed by regulatory experience |
An outsourced DPO provides the independence, expertise and ongoing availability the role requires, without hiring a full-time privacy lawyer.
Our DPO spent five years at Hungary’s National Authority for Data Protection and Freedom of Information (NAIH), gaining first-hand insight into how the authority conducts its investigations.
Today’s privacy questions span law, technology and information security. Our service brings these perspectives together.
Privacy, information security and compliance experts support your registered DPO. Every document undergoes independent peer review before delivery.
We design workable processing arrangements that meet privacy requirements and support your business.
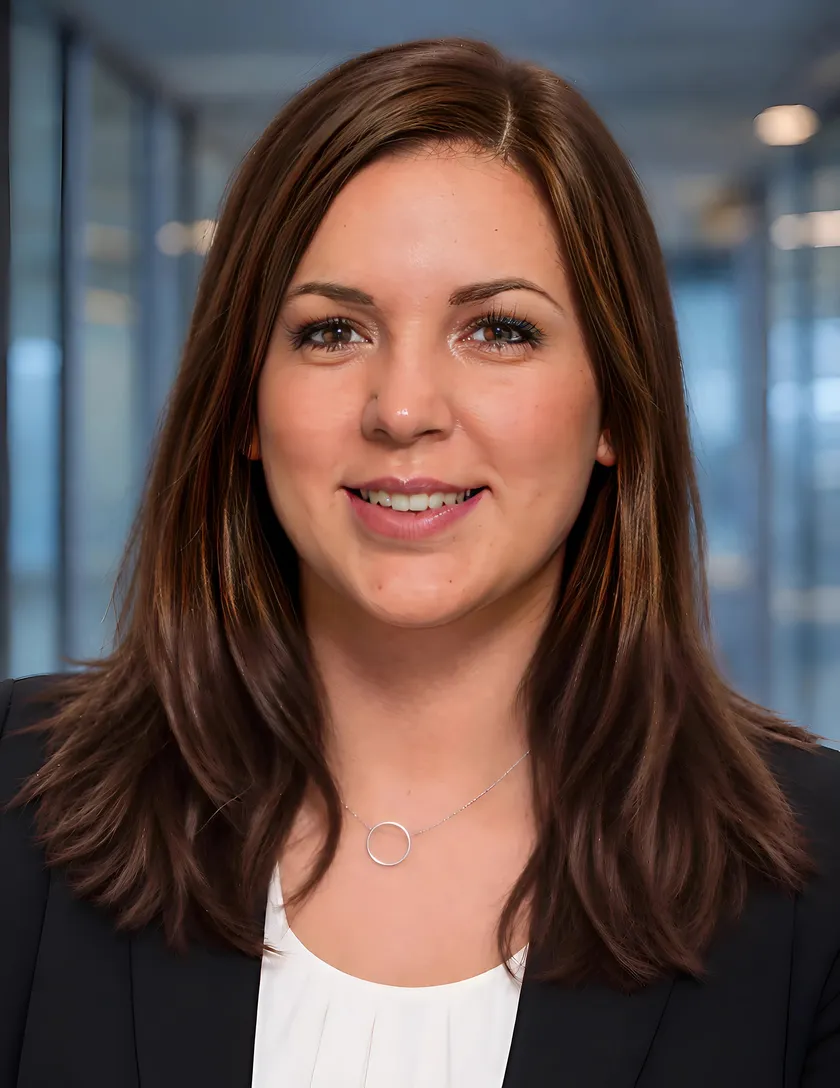
Lawyer and cybersecurity law specialist; privacy and information security adviser, former NAIH expert
Fanni graduated cum laude in law from Pázmány Péter Catholic University, then completed postgraduate studies in cybersecurity law at Széchenyi István University. She spent five years as a data protection expert at NAIH, conducting compliance investigations, assessing requests and complaints, preparing regulatory decisions, cooperating with EU authorities on cross-border cases and developing expert opinions. She understands the evidence regulators expect and where organisations encounter difficulties.
As an adviser and DPO for corporate clients, she develops privacy and information security policies, records and notices, conducts compliance reviews and internal audits, and reviews contracts. She also contributes to NIS2, ISO 27001 and AI Act projects and regularly delivers privacy and security training to employees and management.
“At the authority, I learned that many fines stem from oversights: an unanswered request, a late breach notification or a missing processor agreement. As a DPO, my role is to help prevent these issues and, if they do arise, ensure the organisation is prepared to respond to the authority.”
We assess whether you need a DPO, review your processing activities, any previous regulatory enquiries or breaches, and your current compliance position.
We agree monthly capacity, responsibilities and response times, then provide a tailored fixed-fee proposal.
We prepare the appointment document, NAIH notification and the wording for your website and privacy notices, ready for your approval and signature.
We review your processing records, notices, data processing agreements, breach response and request handling, then provide a prioritised action plan.
Support for requests, breaches and everyday questions, quarterly management reports, annual reviews and training, with prompt expert assistance for regulatory enquiries.
As privacy advisers, we apply the same principles to our own work that we recommend to clients.
A DPO with regulatory experience, without a full-time legal hire.
A free 30-minute consultation and a tailored proposal within 24 hours.